SafeNet/i uses exit point technology to provide complete visibility and control over IBM i access from the network. It protects your system from unwanted and unauthorized activity.
SafeNet Features at a Glance
-
Visibility
Log all activity for vulnerable network connections from FTP, SQL Server, IFS and more
-
Access Control
Create sophisticated user and object based rules to protect critical applications and data
-
Alerting
Instant awareness of access violations with built-in Email, SMS and SIEM alerting
-
Integrated MFA
Add extra protection for powerful users with DUO MFA for Telnet, SQL, FTP and Signon
-
Ransomware
Automatically detect and block potential attacks using IFS activity log pattern matching
-
Security Audit
Built-in reporting simplifies validation of security controls for system network activity
Common IBM i Attack Vectors Protected by SafeNet
-
SQL
Direct SQL connections (ACS, ODBC, others) bypass native OS security, exposing unsecured data and allowing CL access
-
FTP
FTP connections bypass native OS security, exposing data and allowing any user to run system commands
-
IFS
Netserver shares can expose the entire IFS including system folders required to operate the system
SafeNet/i protects your IBM i system from unwanted and unauthorized access via network connections, including the Internet. It lets authorized users do the work they need while keeping unauthorized users out. Modern network connections like Access Client Solutions (ACS), FTP, ODBC and others, can leave the information on your IBM i exposed. SafeNet/i closes this exposure, and it does it without changing your current security configuration.
Did you know ....
- Many Client/Server functions bypass traditional IBM i/OS security checking unless you have fully implemented object level security.
- Without this same full implementation of object level security, a PC-based Client database tool, such as Microsoft Access, can ACCESS any data file on your system.
- That same MS Access user can UPDATE any data file on your system.
- The same MS Access user can even DELETE records or files on your system.
While it is true that you can trust most employees, accidents, not intent, cause most incidents of data loss. Further, if you have implemented traditional IBM i applications using menus and IBM i programming, you may have been required to grant full object authority to many users. You may not want these same users to have full object authority when they access your system via Client Server functions. Using traditional IBM i applications, the application controls how much data access is granted. Object security, however, cannot be as context selective for granting rights to access information.
SafeNet/i enables client/server security on your IBM i using IBM's Exit Points. It supports a variety of controls from simple logging of all activity to completely restricting access to system functions and data. And it does this in a completely non-invasive manner. No changes are made to your existing IBM i/OS security setup. No additional user profiles are needed nor are normal IBM i/OS security features changed or overridden in any way. SafeNet/i is simply an additional layer of security that is placed over standard IBM i/OS security to secure information requests from attached systems.
Check out these features:
- Request Logging - With basic use, SafeNet/i tracks each request coming from a client into the IBM i. It stores this information in a log that you can review. You can see who is accessing your system, which server function on the IBM i they are using, and what data or objects they are using. You can optionally choose to store the logging information in a journal which is tamper proof providing your auditors with absolute assurance that the logs have not been changed.
- Audit Reports - SafeNet/i provides valuable insight about the clients that are connecting to your system. Information includes the version, release and modification level of the licensed programs the clients are using.
- Limit Access to Server Functions, Based on User Profile - SafeNet/i can limit access to specific server functions on the IBM i based on the individual's user profile.
- Exclude Server Functions - SafeNet/i can turn off individual server functions. For example, you can completely exclude the file transfer function for all users on your IBM i.
- Limit Access to Objects within Server Functions, Based on User Profile - SafeNet/i can implement object level security over clients that are accessing the various server functions on the IBM i. Authority is granted by user profile to the individual servers. Then it grants each user authority to objects on the system.
- Control Internet/Intranet Access - SafeNet/i lets you limit Internet/Intranet access to specific workstations and IP addresses that you define. All others are automatically rejected when they attempt to use most server functions on your system. SafeNet/i even lets you set up controlled use of Anonymous FTP on your system.
- Control Remote Commands - SafeNet/i lets you specify which users can submit remote commands to your IBM i and what specific commands they are allowed to use. This control is provided for remote CL commands and for remote FTP commands.
- Context Sentsitive Source IP Address Controls - SafeNet/i lets you control which remote IP addresses can connect with your system by user profile and by server function. Using this feature, a user profile might be granted access to the system for FTP, but denied access for ODBC from a given source IP address (or IP address range). This will allow customers, for example, to limit ODBC connections to users when they are on site and deny similar access when they are working remotely.
- Customer Exit Programs - SafeNet/i gives you control over exit processing for any specific requirements that you have which are not covered by SafeNet/i. Each exit point can optionally call an exit routine that you provide for additional processing that is unique to your installation.
- Time-of-Day, Day-of-Week Controls - shuts down server functions for selected users during non-business hours thereby significantly reducing your security exposure. This can also be extended to specific days of the week and holidays.
- Multifactor Authentication - Add an extra layer of protection for powerful user profiles. MFA is the last line of defense against a compromised user profile. With DUO integration, users must authenticate when connecting via TELNET, FTP, SQL or SIGNON events.
- Ransomware Detection - SafeNet uses pattern matching in IFS Netserver log activity to detect possible ransomware events and automatically block users or even the entire IFS.
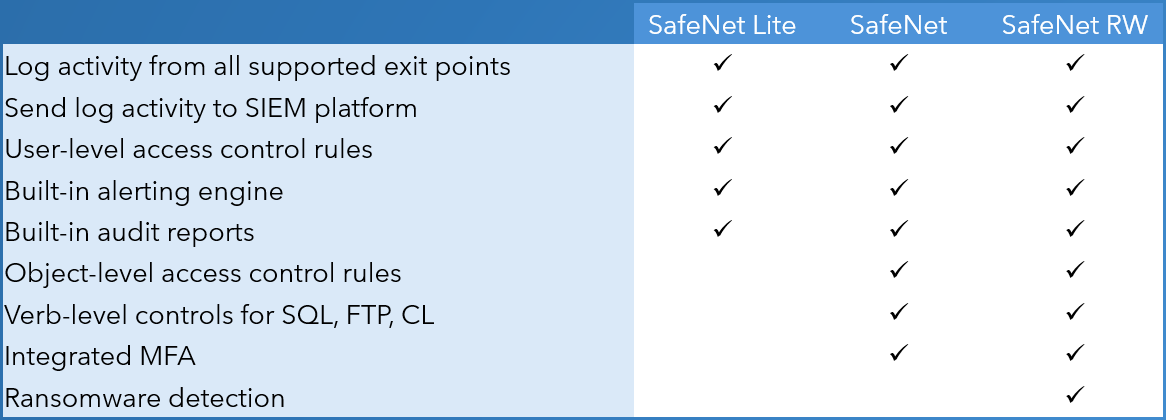
SafeNet Licensing
What Next?
Review this on-line demo then submit this order form to schedule a live demo and start your POC. We look forward to hearing from you. If we can help clarify any SafeNet/i features, please E-mail or call (518) 897-5002.